
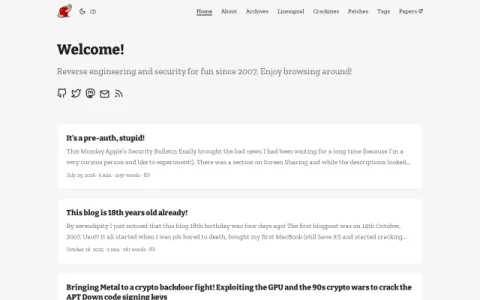
This site is the personal research journal of fG!, started in October 2007 as a place to document reverse engineering and security experimentation, primarily on Apple platforms. It has grown into an archive of nearly two decades of posts, from early Mac cracking notes to modern vulnerability analysis.
The core content is technical write-ups: analyses of pre-auth bugs, Screen Sharing vulnerabilities, patches, crackmes, and papers. Posts often walk through the discovery and testing process in detail, including code, debugging steps, and commentary on vendor responses, which makes them useful as case studies rather than quick tutorials.
It is aimed at reverse engineers, security researchers, and macOS/iOS developers who already understand binaries, assembly, and exploitation basics. Readers looking for introductory material or regularly updated news will find the pace and depth demanding, and the publishing cadence is irregular.
A practical approach is to browse the archives and tags for a specific platform or bug class, then read the related patches and papers together. Treat it as a reference library of hard-won field notes rather than a structured course, and expect to supplement it with your own tooling practice.

评论与评分
0还没有评论,来写下第一条评价吧。