
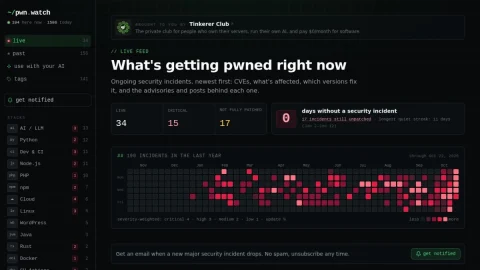
pwn.watch is a live incident feed rather than a static vulnerability database. The homepage opens with a running count of active incidents and a severity split, then lists them newest first, so a visitor immediately sees what is being exploited at this moment instead of browsing an archive.
Each entry ties a CVE to the affected stack, the patch status (patched, partial, or unpatched), the fixed versions, and the advisories and community posts that surfaced it. A tag rail covers AI/LLM, Python, Node.js, PHP, npm, Docker, GitHub Actions, Linux, WordPress, and other common stacks, and incidents can be filtered by patch status or severity.
The site suits developers, sysadmins, and security engineers who need a quick read on whether something they run is currently under attack. It is less suited to people wanting full technical write-ups or remediation steps, since the value is in aggregation and linking out to primary sources.
Practically, use the stack tags to build a short watchlist of the technologies in your environment, check the unpatched and partial counts first, and subscribe to the email alerts for major incidents. The RSS, JSON, and llms.txt feeds make it easy to pipe into a dashboard or an AI assistant. Treat it as an early-warning layer that points you to the advisories worth reading in full.
评论与评分
0还没有评论,来写下第一条评价吧。