
Kevin Coleman’s site is a personal publishing space for a software professional who writes about solving business problems through software. Rather than a product or service page, it collects first-person essays, project notes, and opinion pieces that reflect the author’s day-to-day work and technical judgment.
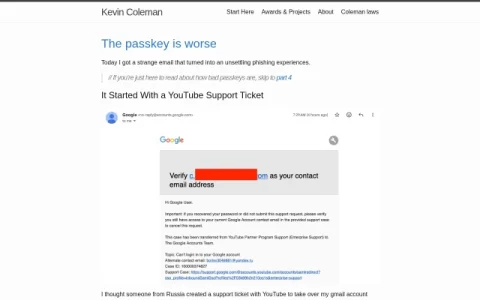
The strongest content is security-focused storytelling. A long post walks through a phishing email that impersonated a YouTube support ticket, a convincing Google login page, and a failed two-factor flow that led into an Apple passkey prompt. The narrative shows how attackers exploit routine authentication habits and where passkeys introduce friction.
Other sections include awards and projects, an about page, and a set of informal “Coleman laws” capturing lessons learned. These give context on the author’s background and the kind of engineering and product thinking behind the writing.
This site suits software engineers, security-minded product people, and anyone who wants a practitioner’s view of authentication and phishing risks. Read the security essays first, and treat the rest as background on the author’s approach.

评论与评分
0还没有评论,来写下第一条评价吧。