
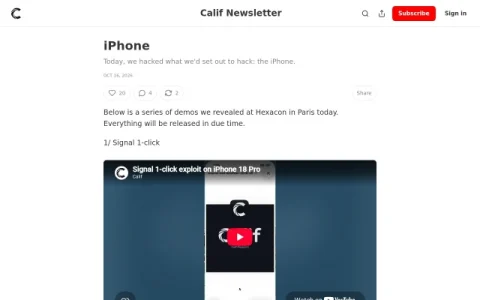
Calif Newsletter is a Substack publication from Calif Global Inc. that documents the team’s security research as short, first-person posts. Rather than general commentary, it centers on work the authors present at conferences, with the iPhone post collecting the demos they unveiled at Hexacon in Paris.
The format is deliberately minimal: a brief framing sentence followed by a numbered list of demo titles, such as a one-click Signal scenario and an iMessage-focused item. The post states that everything will be released in due time, so the page functions as an announcement index rather than a technical deep dive with code or methodology.
It is aimed at offensive security researchers, exploit developers, and technically literate readers who want early notice of Calif’s published work and conference appearances. General audiences looking for consumer privacy advice or step-by-step iPhone hardening tips will find little actionable material here.
A practical approach is to subscribe so new releases and follow-up posts arrive directly, then revisit the numbered demos once the corresponding write-ups or tools are published. Treat the list as a table of contents for future material, and check the comments for reader discussion.
In short, it is a lightweight research bulletin worth following for disclosure timing, not a standalone tutorial.

评论与评分
0还没有评论,来写下第一条评价吧。