
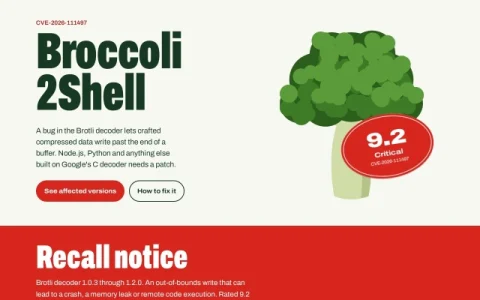
Broccoli2Shell documents CVE-2026-111497, a memory-safety flaw in Google’s Brotli decoder that permits crafted compressed data to write past the end of a buffer. The site frames the issue as a recall notice: decoder versions 1.0.3 through 1.2.0 are affected, with outcomes ranging from crashes and memory leaks to remote code execution. GitHub rates it 9.2 Critical under CVSS 4.0, while Node.js classifies it as High.
The core of the page is a remediation matrix. Each product line is paired with the release that fixes it: Google Brotli C library 1.0.10, 1.1.1 and 1.2.1; Node.js 26.12.1, 24.22.1 and 22.23.4; Python Brotli 1.2.1 and brotlicffi 1.2.1.0. Node.js 25, 23, 20 and older receive no fix at all, and the site directs users on those end-of-life lines to migrate to 22, 24 or 26.
Beyond version numbers, the advisory stresses operational follow-through. Installing an update does not protect a process that is already running, because it retains the old decoder until restarted. Containers need their base image rebuilt on a patched foundation and redeployed. Separate sections cover who is exposed, bundled copies of the decoder inside other software, how to check, and the exploitation timeline.
This resource suits backend and platform engineers, security responders and maintainers who ship Node.js or Python services with Brotli compression enabled. It is also useful for anyone auditing dependencies that vendor the C decoder. Readers should confirm their exact runtime and library
Comments & Ratings
0No comments yet. Be the first to review.