
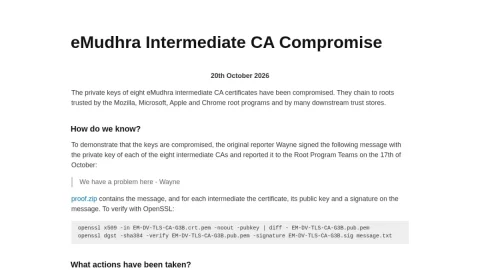
The site is a focused disclosure page about the compromise of eight eMudhra intermediate CA certificates. It states that the private keys chain to roots trusted by Mozilla, Microsoft, Apple and Chrome root programs as well as many downstream trust stores, and it records the date of the report as 20 October 2026.
The page provides verifiable evidence rather than bare claims. It explains that the original reporter, Wayne, signed a message with the private key of each of the eight intermediate CAs and reported the issue to Root Program Teams on 17 October. A proof archive contains the message, each certificate, its public key and a signature, and the page includes OpenSSL commands to check the public key and verify the signature.
It also summarizes remediation. Firefox and Chrome blocked the certificates from 17 October, Apple devices from 19 October and Microsoft platforms from 20 October, and the issue was responsibly disclosed to downstream trust stores. This makes the page useful for PKI engineers, certificate authority auditors, trust store maintainers and security researchers who need primary-source details.
For best use, read the timeline alongside the proof files and reproduce the OpenSSL verification independently. Treat the page as an incident record and technical reference rather than a general news article, and check root program announcements for the latest status.

Comments & Ratings
0No comments yet. Be the first to review.