
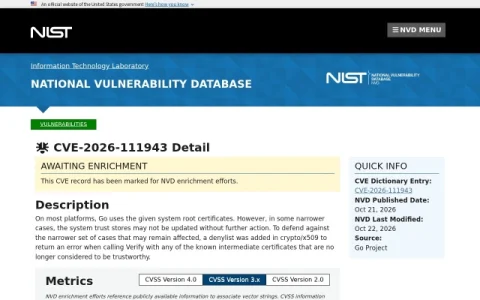
NVD is the National Vulnerability Database maintained by NIST, serving as the U.S. government’s authoritative source for standards-based vulnerability management data. Each entry, such as the CVE detail page referenced here, consolidates the CVE identifier, description, publication dates, and current analysis status in one place.
The core value lies in structured enrichment: CVSS base scores and vectors, CWE weakness classification, CPE configurations that indicate affected products, and curated reference links to advisories and patches. This makes records comparable across vendors and useful for prioritization rather than raw disclosure alone.
It is primarily used by security analysts, vulnerability management teams, system administrators, and researchers who need canonical identifiers and severity context. Developers and compliance teams also rely on NVD data to map findings to known weaknesses and affected product versions.
Because NVD records can lag behind vendor advisories and analysis status varies by entry, it is best treated as a reference layer rather than a live scanning tool. Cross-check vendor advisories for patch guidance, and note that API access and data feeds are available for programmatic use.
Comments & Ratings
0No comments yet. Be the first to review.