

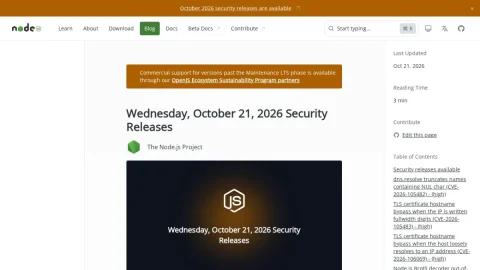
This page is an official Node.js project announcement documenting security releases published on October 21, 2026. Rather than a general product page, it is a targeted advisory aimed at users of specific Node.js release lines who need to know which versions contain fixes and what was addressed.
The announcement lists updates for the 26.x, 24.x, and 22.x release lines, including dependency bumps to c-ares, ca-cert, OpenSSL, SQLite, and Undici. It then details individual vulnerabilities with CVE identifiers and severity levels, such as a high-severity issue where dns.resolve truncates names containing a NUL character, and a TLS certificate hostname bypass when an IP is written in fullwidth digits.
It is written for Node.js developers, platform engineers, and security or DevOps staff responsible for runtime upgrades. Readers already familiar with Node.js release terminology will get the most from it, since it assumes knowledge of LTS lines and semantic versioning.
Practical use: check whether your deployed version falls in an affected line, read each CVE entry to judge exposure, then upgrade to the patched release and re-run your dependency and TLS configuration checks. Cross-reference with the official release notes before rolling out to production.
In short, it is a concise, authoritative patch notice rather than a learning resource, and should be treated as an action item for teams running affected Node.js versions.

Comments & Ratings
0No comments yet. Be the first to review.