
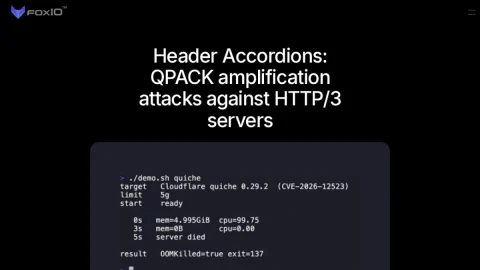
FoxIO is a cybersecurity company focused on solving difficult cyber challenges through original research and practical technology. Its blog serves as a publication channel for detailed security findings, tooling updates, and protocol-level analysis rather than general industry news.
The site’s core content includes in-depth vulnerability research, such as the QPACK amplification attack write-up covering affected HTTP/3 libraries, CVE identifiers, fixed versions, and mitigation guidance. Posts are technical and evidence-driven, often including test results and actionable remediation steps.
This makes FoxIO most useful for security researchers, network engineers, and developers working with protocols like HTTP/3 and QUIC. Readers looking for concise summaries or beginner-friendly explanations may find the material dense, but practitioners will appreciate the specificity.
When using the site, check publication dates and patch status carefully, since vulnerability information changes over time. Cross-reference CVEs and vendor advisories before acting on mitigations. Overall, FoxIO is a credible source for focused, original cybersecurity research.
Comments & Ratings
0No comments yet. Be the first to review.