
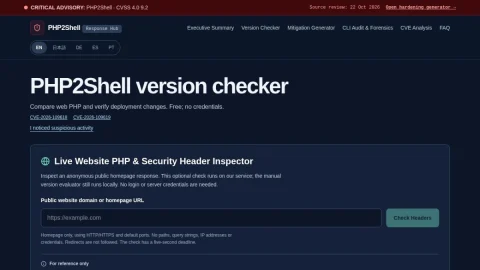
PHP2Shell Response Hub is a focused advisory site built around two CVEs, CVE-2026-109618 and CVE-2026-109619, rated CVSS 4.0 9.2. Rather than a general security portal, it concentrates on helping teams determine whether their PHP deployments are affected and what to do next. The site is organized into an executive summary, version checker, mitigation generator, CLI audit and forensics guidance, CVE analysis, and an FAQ.
The version checker compares your web PHP version against official patch levels and lets you verify deployment changes after remediation. An optional live inspector reads only passively broadcast HTTP response headers from a public homepage, using HEAD or GET with no paths, credentials, or redirects, and a five-second deadline. The mitigation generator produces environment-specific hardening steps, while the CLI audit and log forensics material supports post-incident review and detection rule creation.
This resource is aimed at system administrators, DevOps engineers, and developers responsible for PHP fleets who need fast exposure triage during a critical advisory window. Security analysts handling incident response may also find the forensics and detection sections useful when correlating logs.
Use the manual version evaluator first, since it runs locally and requires no credentials. Treat the header inspection as a reference signal only: it cannot detect internal php.ini runtime mitigations, so confirm patch status directly on the host. Generate mitigati

Comments & Ratings
0No comments yet. Be the first to review.