
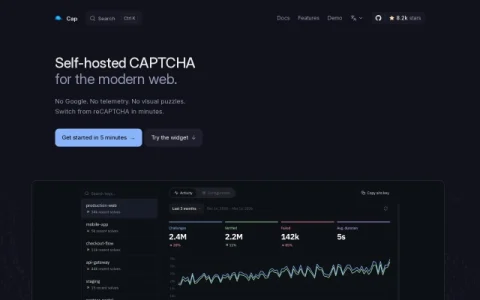
Cap positions itself as a self-hosted replacement for reCAPTCHA and hCaptcha, built for sites that would rather not send visitor data to Google or other third parties. The project is open source under Apache 2.0 and has gathered a sizable GitHub following, which signals active community interest in privacy-first bot mitigation.
The core design runs two independent layers. A proof-of-work layer uses SHA-256 via WASM or GPU-resistant time-lock challenges, while instrumentation challenges are server-generated JavaScript that verifies the browser environment through DOM operations. There are no image grids or audio puzzles for users to solve, and the widget is roughly 20kb with zero dependencies, so it loads quickly.
Because Cap is self-hosted, operators control where challenge data lives and can avoid third-party network calls entirely. The project reports zero telemetry and positions itself as a quick switch from reCAPTCHA, with a setup path measured in minutes rather than days. Documentation, a live demo, and multi-language pages are available from the site.
Typical users are developers and small teams running their own servers who want CAPTCHA protection without visual friction or vendor lock-in. Before adopting it, check that your stack can host the service, review the agent and LLM documentation pages for accurate technical details, and test the widget against your traffic patterns. Cap is a solid fit when control and privacy matter more than a fully managed service.

Comments & Ratings
0No comments yet. Be the first to review.