
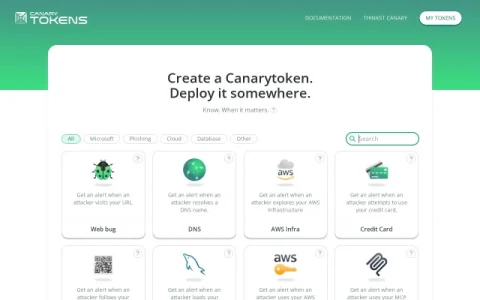
Canarytokens is a free, open-source-style service from Thinkst that flips breach detection around: instead of waiting to discover an intrusion, you plant tokens that announce themselves when someone interacts with them. Each token is a small trap placed in a network, file, or cloud account, and any trigger sends you a notification with details about what fired.
The token catalog covers common attack paths. You can generate DNS and HTTP tokens for network canaries, fake AWS credentials that alert on use, cloned website tokens that catch credential phishing, and document tokens such as Word or PDF files that report when opened. Windows directory and SQL Server tokens extend coverage into internal systems, and each token comes with simple placement instructions.
It is aimed at security engineers, sysadmins, and developers who want lightweight early-warning coverage without deploying an agent or standing up infrastructure. Small teams and hobbyist homelabs use it to watch for lateral movement, while larger organizations scatter tokens across segments as a low-cost complement to existing detection.
To get value, place tokens where real activity should never occur, such as unused admin accounts, internal shares, or decoy documents, and route alerts to a monitored inbox. Review triggered tokens regularly and rotate them after any alert. It is best treated as one signal among several rather than a standalone security program.

Comments & Ratings
0No comments yet. Be the first to review.