
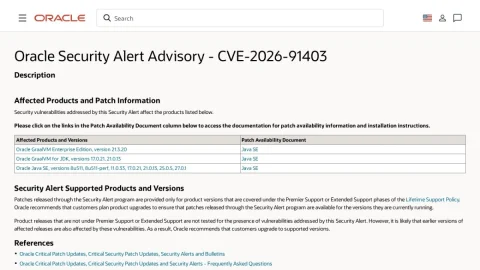
This page is an official Oracle Security Alert Advisory dedicated to CVE-2026-91403. It serves as the primary vendor source for understanding which Oracle products are affected by this vulnerability and where to obtain the corresponding fixes.
The core content is a table of affected products and versions, covering Oracle GraalVM Enterprise Edition 21.3.20, Oracle GraalVM for JDK 17.0.21 and 21.0.13, and Oracle Java SE releases including 8u511, 11.0.33, 17.0.21, 21.0.13, 25.0.5, and 27.0.1. Each row links to a Patch Availability Document with installation instructions.
The advisory is aimed at system administrators, Java developers, DevOps engineers, and security and compliance teams running Oracle Java or GraalVM in production. It is also relevant to organizations that need documented evidence of vendor patch guidance for audits.
Users should confirm whether their deployed versions fall within the listed ranges, then follow the linked patch documents. Oracle notes that patches under the Security Alert program apply only to versions in Premier Support or Extended Support, so planning an upgrade is advisable for older releases.
In short, it is a concise, authoritative reference for assessing and remediating exposure to CVE-2026-91403 in Oracle Java and GraalVM environments.
Comments & Ratings
0No comments yet. Be the first to review.