
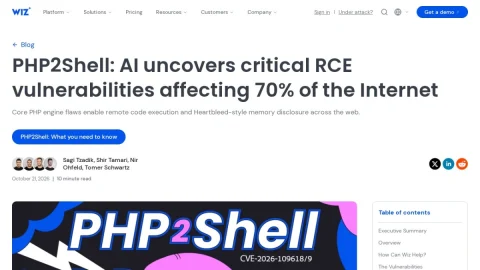
Wiz Blog is the research and content arm of Wiz, a cloud security platform. This page hosts a threat research report on PHP2Shell, a set of critical vulnerabilities found in the core PHP engine rather than in any single application. The post is aimed at readers who need to understand a widely impactful web security issue.
The report describes memory disclosure and unauthenticated remote code execution flaws in PHP itself, noting that every PHP release in the past decade is affected by at least one issue. It frames the risk around the many platforms built on PHP, including WordPress, Joomla, Drupal, and MediaWiki, and summarizes what defenders should know.
The content is written for security researchers, incident responders, and engineering teams responsible for PHP-based infrastructure. It assumes some familiarity with vulnerability terminology and prioritizes scope and impact over step-by-step remediation guidance.
Readers should treat the post as a starting point for exposure assessment and consult official PHP advisories and vendor patches for remediation details. Overall, it is a concise research briefing on a high-impact web security topic.
Comments & Ratings
0No comments yet. Be the first to review.