
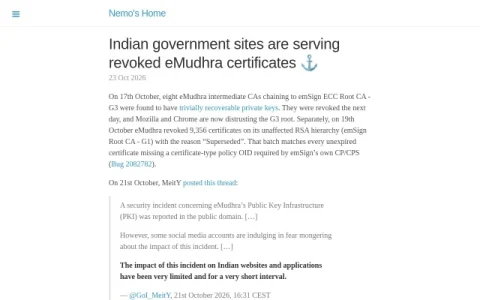
Nemo’s Home is a personal technical blog that focuses on digital security, certificate authorities, and the public key infrastructure underpinning government and enterprise websites. Rather than general commentary, it publishes detailed incident write-ups that follow certificate revocations, root distrust decisions, and the policy documents behind them.
The site’s core strength is primary-source analysis. Posts quote bug trackers, CA policy documents, and official statements, then compare them against observed certificate data. The eMudhra/emSign article is typical: it reconstructs a timeline of key compromise, revocation batches, and browser vendor responses, and it checks official claims against the underlying records.
Readers best served here are security engineers, PKI and compliance specialists, and researchers who need precise accounts of CA incidents. General audiences may find the material dense, since it assumes working knowledge of certificate chains, policy OIDs, and trust stores.
Use the archive and RSS feed to follow updates, and treat individual posts as starting points for incident research rather than tutorials. The blog is a solid reference for anyone who needs to verify how certificate trust failures unfold in practice.
Comments & Ratings
0No comments yet. Be the first to review.