

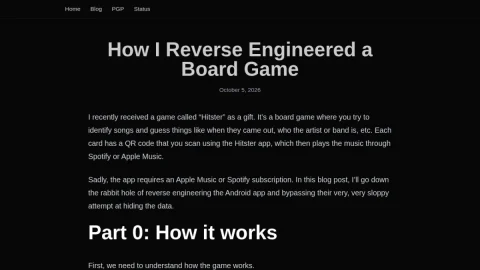
Wuemeli is a personal technical blog that focuses on reverse engineering, security research, and software internals. Posts are written as detailed walkthroughs, sharing the author’s process, tools, and findings rather than just conclusions.
The featured article covers reverse engineering the Android app for the Hitster board game. It explains how the game maps QR codes to music tracks, then digs into the app to bypass its subscription requirement and poorly hidden data. The post includes concrete steps, code-level observations, and commentary on the app’s weak obfuscation.
The site suits developers, security enthusiasts, and curious tinkerers who want to learn practical reverse engineering techniques through real examples. Readers should have some familiarity with Android tooling and basic programming concepts to follow along.
Use the blog as a learning resource: read the walkthroughs sequentially, try the techniques on your own projects, and note the author’s methodology for inspecting apps and APIs. Content is technical and occasionally opinionated, so verify findings independently.
Overall, Wuemeli offers an informative, experience-driven look at reverse engineering that rewards readers who enjoy hands-on technical exploration.
Comments & Ratings
0No comments yet. Be the first to review.