
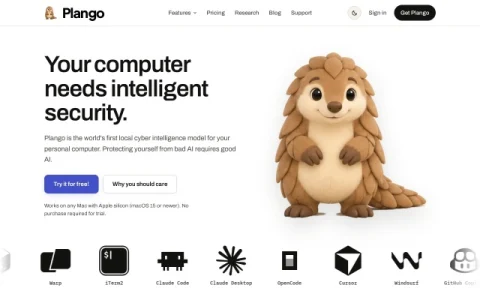
Plango positions itself as a local cyber intelligence layer for personal computers, starting with the Mac. Rather than presenting another dashboard of raw system logs, it translates security posture into plain-English findings, so a non-specialist can understand what is exposed and what to change. The product is built around the idea that protecting against risky AI requires capable AI running locally.
The feature set splits into two halves. On the developer side, it watches coding agents and flags dangerous actions, inventories every MCP server your tools connect to, vets skills, commands, and plugins before an agent trusts them, and moves plain-text keys out of .env files into the Keychain. On the Mac side, it warns before you type a password into a fake login page, shows which apps can reach the camera, microphone, screen, and keystrokes, and maps outbound connections so unwanted traffic can be blocked.
It is aimed at developers who run coding agents and MCP-based tooling, and at privacy-minded Mac owners who want visibility without sending data to a cloud service. The on-device model means files and prompts stay on the machine, which is the main reason to choose it over hosted scanners.
Practical use: install on an Apple silicon Mac running macOS 15 or newer, run the initial audit, then work through the plain-English findings starting with secrets and agent permissions. A trial is available without purchase, so you can confirm coverage of your particular agent stack be

Comments & Ratings
0No comments yet. Be the first to review.