
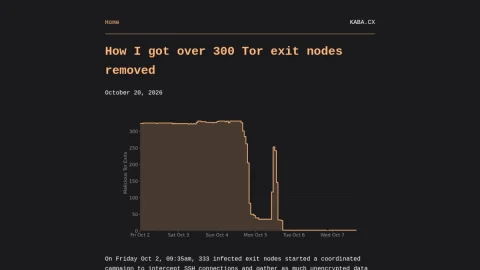
KABA is a personal blog that publishes technical security write-ups, and this post documents a coordinated campaign in which 333 infected Tor exit nodes attempted to intercept SSH connections and collect unencrypted data. The author frames the incident with scale context, noting that roughly 10% of all Tor exit relays were under attacker control.
The core of the article explains how attackers gained server access two months before the campaign, deployed the Ebury 1.8.3 OpenSSH backdoor and credential stealer, and configured exit nodes to favor unencrypted mail traffic while silently redirecting SSH sessions on port 22. It walks through the attack mechanics and the process of getting the malicious relays removed.
The post is aimed at Tor relay operators, incident responders, and security-minded readers who want a first-hand account of detecting and mitigating compromised exit infrastructure. It assumes some familiarity with Tor circuits and SSH.
Readers can use the write-up as a reference for spotting similar exit-node abuse and for understanding how coordinated takedown efforts unfold. It is a focused incident report rather than a general Tor tutorial, best read alongside the linked victim analysis.

Comments & Ratings
0No comments yet. Be the first to review.