
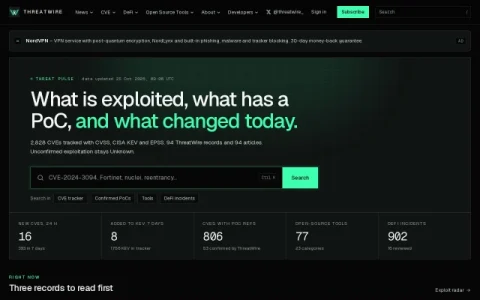
ThreatWire positions itself as a public threat intelligence wire rather than a general security news site. Its organizing question is practical: what is being exploited, what has a working proof of concept, and what changed today. Every record is built around that framing, so readers can move from a headline to a structured vulnerability entry without hunting across multiple sources.
The core of the site is a CVE tracker that pairs each entry with CVSS severity, CISA KEV status and EPSS scores, then adds PoC references with a confirmed or unconfirmed marker. Alongside this sit open-source security tools and a DeFi incidents section, giving coverage to both traditional enterprise vulnerabilities and on-chain exploits. A threat pulse panel surfaces new CVEs, recent KEV additions and freshly confirmed PoCs.
The editorial approach is the differentiator: reporting separates confirmed facts from unknowns, and unconfirmed exploitation stays labeled Unknown rather than being implied. This suits security analysts, vulnerability managers, SOC teams and DeFi protocol watchers who need defensible prioritization data, not just awareness.
Use it as a daily triage layer: check the threat pulse for what changed in the last 24 hours, then open individual CVE records to compare KEV deadlines against EPSS likelihood and PoC availability. Because records cite their sources, it also works as a starting point for internal reporting. It is a focused intelligence feed, not a full vulnerability sc
Comments & Ratings
0No comments yet. Be the first to review.