
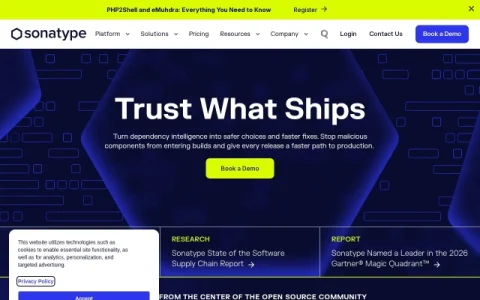
Sonatype is a software supply chain security company best known as the creator of Nexus Repository, a widely used artifact repository manager. The platform is built around the idea of trusted components: it helps organizations understand what open source and AI-generated code goes into their software and whether those components are safe to ship.
The product line covers the full lifecycle of dependency management. Nexus Repository stores and distributes build artifacts, while Lifecycle performs software composition analysis and automated remediation. Firewall blocks malicious open source packages, Guide supports dependency decisions in AI builds, and SBOM Manager automates compliance reporting. These tools integrate with common CI/CD pipelines and support flexible deployment options.
The site serves developers, DevOps engineers, and security teams, along with organizations in regulated industries such as government, financial services, and healthcare that need license compliance and software supply chain visibility. Enterprise buyers will also find industry-specific solution pages and support information.
A practical starting point is to explore the product pages for Nexus Repository and Lifecycle, then check the integrations and language support to confirm fit with your existing toolchain. Teams evaluating AI governance can look at the dedicated AI & LLM governance section. Overall, Sonatype is a mature choice for organizations that treat open source risk as a first-class

Comments & Ratings
0No comments yet. Be the first to review.