

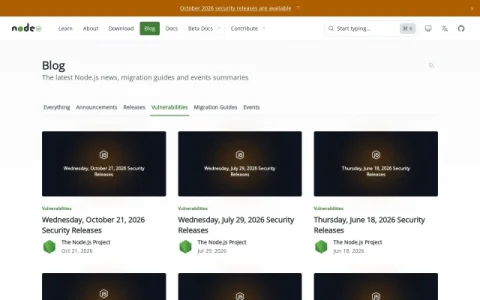
The Node.js Blog is the official editorial channel of the Node.js project, hosted on nodejs.org. It collects project announcements, release notes, vulnerability disclosures, migration guides, and event summaries in one chronological feed, with category filters for Everything, Announcements, Releases, Vulnerabilities, Migration Guides, and Events.
The vulnerabilities category is the most operationally important section. Posts such as the recurring “Security Releases” entries dated October 21, 2026, July 29, 2026, June 18, 2026, and March 24, 2026 announce patched versions and affected release lines, while the OpenSSL Security Advisory Assessment from January 2026 explains how upstream advisories map to Node.js. Longer technical pieces, like Joyee Cheung’s article on designing a minimally HashDoS-resistant yet quickly reversible integer hash for V8, document the reasoning behind low-level fixes.
The blog serves backend and platform engineers, security and compliance teams, and release managers who must decide when to upgrade production runtimes. Contributors and package maintainers also use migration guide posts to plan breaking-change adoption across major versions.
A practical approach is to filter by Vulnerabilities and check the publication date against your supported Node.js lines, then read the linked release notes before scheduling upgrades. Announcements and Events posts are useful for community planning but less urgent. Overall, the blog functions as the project’s o

Comments & Ratings
0No comments yet. Be the first to review.