

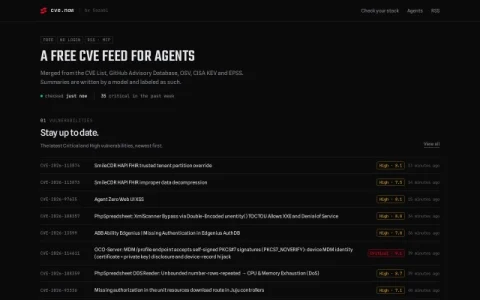
cve.now is a lightweight public feed built for people and software agents that need to track newly disclosed vulnerabilities without maintaining their own aggregation pipeline. It pulls from the CVE List, GitHub Advisory Database, OSV, NVD, ENISA EUVD, CISA KEV, EPSS and Exploit-DB, then presents a single stream of Critical and High severity entries ordered newest first.
The feed is available as RSS, Atom and JSON Feed, plus an MCP endpoint for agent integration. Each entry shows the CVE identifier, affected package or project, severity score, a short plain-language summary and whether a fix is available. Summaries are generated by a model and labeled as such, so readers know which text is machine-written rather than sourced from the advisory.
The interface includes filters for technology and package ecosystem, letting you narrow the stream to the stacks you actually run. A status line indicates when the feed was last checked, which helps gauge freshness. No account or login is needed, and the service is free.
It is aimed at security engineers, DevOps and platform teams, open-source maintainers and developers who want a low-effort watchlist, as well as agent builders who need structured vulnerability input. For deeper context, cross-reference the linked original advisories before acting.
Use it as an early-warning layer rather than a replacement for formal vulnerability management, and verify severity and exploitability against primary sources before prioritizing remediat
Comments & Ratings
0No comments yet. Be the first to review.